Critical PHP Vulnerabilities Threaten Over 70% of the Internet
Translated & summarized from N12 by baba
Two critical security flaws in the PHP programming language, which powers approximately 70% of the internet, have been discovered, allowing remote server takeover. Global cybersecurity agencies have issued urgent warnings, with many governments and organizations taking servers offline as a precaution. Patches have been released, and immediate updates are strongly recommended to prevent widespread attacks and data breaches. The vulnerabilities were found with the assistance of AI, highlighting its role in both discovering and potentially exploiting security weaknesses.
The story in 6 lines · by baba
- Critical PHP vulnerabilities allow remote server takeover, affecting an estimated 70% of the internet.
- Global cybersecurity agencies have issued urgent warnings and recommended immediate server updates or disconnection.
- AI played a key role in discovering these flaws, which have existed for over a decade.
- Widespread system shutdowns have occurred in several countries as a precautionary measure.
- Millions of servers are running unsupported PHP versions, increasing their vulnerability.
- Immediate patching and multi-layered security are advised to mitigate risks.
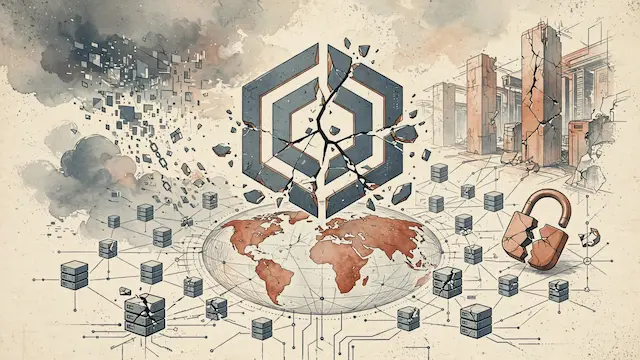
Two severe security flaws, dubbed PHP2Shell, have been discovered in the PHP programming language, which powers an estimated 70% to 75% of the world's websites. These vulnerabilities allow remote code execution and server takeover without the need for passwords or administrative privileges, earning them a critical CVSS score of 9.2. The flaws were identified with the help of artificial intelligence and disclosed recently, prompting urgent warnings from global cybersecurity agencies.
Governments and major organizations worldwide are taking precautionary measures, including taking servers offline. The Israel National Cyber Directorate has also urged immediate updates to PHP environments. Experts warn that all servers using PHP versions from the last 20 years are potentially vulnerable, impacting a vast portion of the internet. Official security patches were released on October 21, 2026, with the PHP Foundation imploring all users to update immediately.
Intelligence and cybersecurity agencies, including the NSA, NCSC in the UK, and the FBI, have issued strong advisories. The NSA recommended immediate updates or taking systems offline if an update is not feasible. The FBI advised immediate patching, scanning for suspicious activity, and isolating systems in case of a breach. Similar warnings and recommendations have been issued by agencies in Japan, the Netherlands, and CERT-EU.
The vulnerabilities, which existed in PHP's error handling and memory management for over a decade, were discovered independently by the Calif group and Israeli company Wiz, both utilizing AI tools. Wiz highlighted that AI has significantly lowered the barrier to exploiting these complex flaws, which were previously difficult to leverage. OpenAI, which led a coalition to prepare the fixes, stated this marks a milestone in AI's ability to find impactful bugs at an internet scale.
Early signs of exploitation have been reported by Cloudflare and Amazon, with researchers from Palo Alto Networks identifying over 22.6 million potentially vulnerable instances. Wiz noted that while the flaws have existed for years, AI advancements enabled their simultaneous discovery by multiple researchers. Organizations are urged to update their PHP servers or disconnect them from the internet until patches are applied. The discovery underscores the dual nature of AI in both finding and exploiting vulnerabilities.
The severity of the flaws has led to widespread system shutdowns in countries like the Netherlands, Finland, France, and Denmark, affecting government services, ports, and educational platforms. Wikipedia and the Internet Archive also took systems offline for maintenance. Experts emphasize that these shutdowns are often a responsible protective measure during the patching process, not necessarily an indication of a breach.
Estimates suggest around 1.5 million hosts running PHP are using unsupported versions (8.1 and older) for which official patches are unavailable, though some vendors offer custom fixes. Companies like Automattic (WordPress, Tumblr) have stated their services are protected, while Israeli company Wix and Squarespace are unaffected as they do not use PHP. Small websites and shared hosting environments are considered particularly at risk. Security experts advise implementing multiple layers of defense to prevent secondary attacks like phishing and malware distribution, even after patching.
Mentioned
The same event, reported separately by each outlet. Open a few to compare what different newsrooms emphasize — and what they leave out.
Centre 1Right 1
Not the same event — other stories that share this one’s people, places, or theme: background, reactions, and follow-ups.