
Meitav Trade Faces Data Breach After Third-Party API Vulnerability
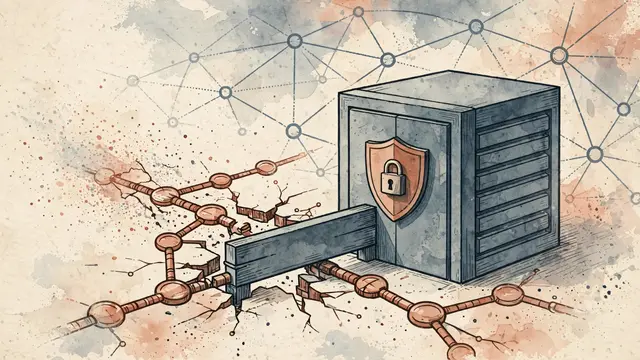
Meitav Trade, an Israeli investment house, experienced a cyberattack attempt over the weekend targeting thousands of customer accounts. The breach occurred when a security vulnerability was discovered in one of the external API interfaces managed by a third-party supplier. Attackers sent approximately 3,000 one-time verification code text messages to customers without their request, and made a few unsuccessful attempts to change the phone number receiving the codes.
The company immediately blocked the compromised API interface, halting its use and preventing further unauthorized activity. Meitav Trade stated that customers whose personal information was accessed would be notified. The company's systems are reportedly functioning normally with no known limitations.
According to Gil Messing, Head of Staff and Global Communications at Check Point, the attack exploited a common vulnerability through a third-party supplier, rather than directly breaching Meitav's main systems. He explained that an organization's attack surface now extends to its suppliers, cloud services, and external entities with access to its data.
The attackers managed to extract personal information from a limited number of customers, including full name, ID number, and bank account details. Meitav emphasized that customer funds, trading accounts, and passwords were not exposed, and no access to trading systems was gained. Einat Miron, a business cyber risk expert, raised concerns about the potential for future misuse of the stolen data for impersonation or targeted fraud, questioning the extent of the breach and the company's responsibility towards affected clients.
Meitav Trade has reported the incident to the National Cyber Directorate and the Privacy Protection Authority as required by Israeli privacy laws. Customers are advised to be vigilant against suspicious messages, avoid sharing verification codes or personal details, and refrain from clicking on links in unsolicited SMS or emails, as the leaked information could be used for phishing and scams.
The same event, reported separately by each outlet. Open a few to compare what different newsrooms emphasize — and what they leave out.


Not the same event — other stories that share this one’s people, places, or theme: background, reactions, and follow-ups.

Ask About This Article
Duki reads it, and every newsroom on the same story, then answers with sources.
How the headlines differ
News Plus
One Event. Different Headlines.
See the words each newsroom chose, with the original headline beside the translation.